DevSecOps: CI/CD with security by design
Bringing security into every stage of the lifecycle reduces cost, risk and delivery time.
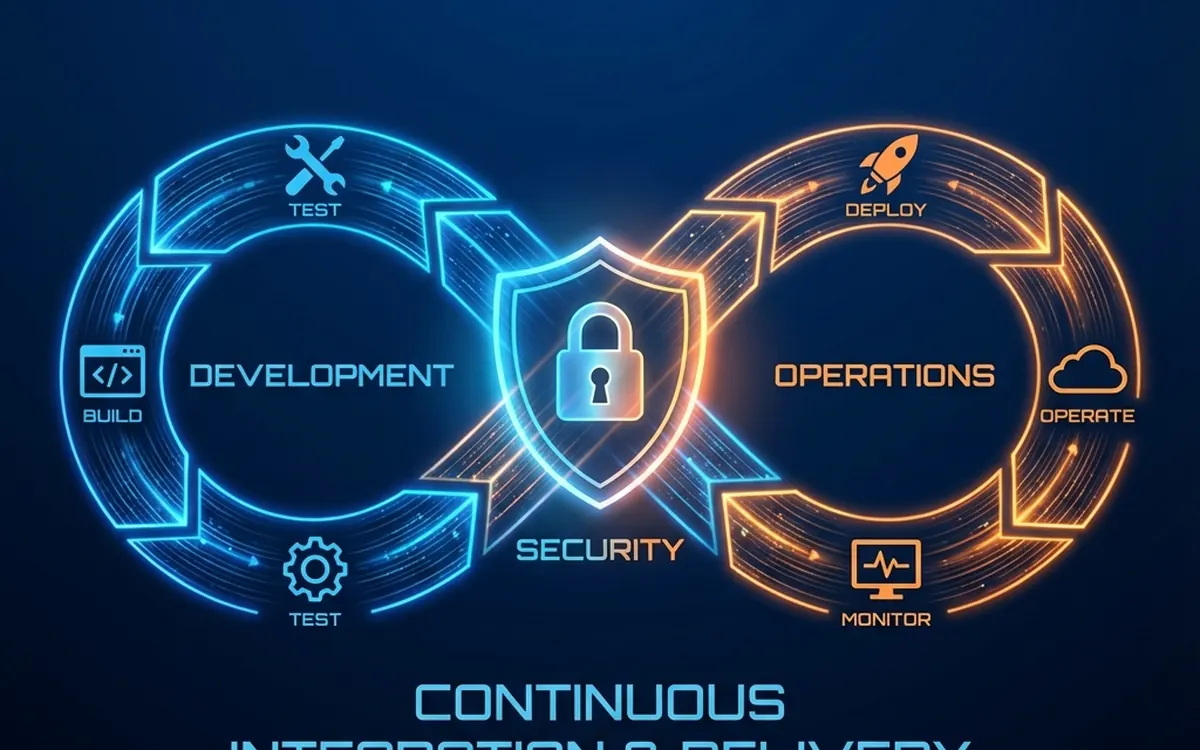
DevSecOps integrates security into every stage of the software lifecycle, from design to deployment. This shift-left approach finds and fixes vulnerabilities early, when they are cheapest to fix.
Modern CI/CD pipelines include static analysis (SAST), dependency analysis (SCA), dynamic testing (DAST) and container image scanning. Automating these checks keeps insecure code out of production.
Policy as code, secrets management and rotation, artifact signing and continuous auditing complete a solid security posture for teams that ship fast.
Breitner Enrique González AngaritaHead of Architecture & Development · IFX Networks